
Develop and maintain an Incident Response Plan (IRP) outlining roles, responsibilities, and escalation procedures.
Establish an Incident Response Team (IRT) to handle security breaches effectively.
Conduct regular tabletop exercises and penetration testing to assess response readiness.
Implement a structured post-incident review process to identify lessons learned and improve future response efforts.
Coordinate with external cybersecurity partners, law enforcement, and regulatory bodies during major incidents.
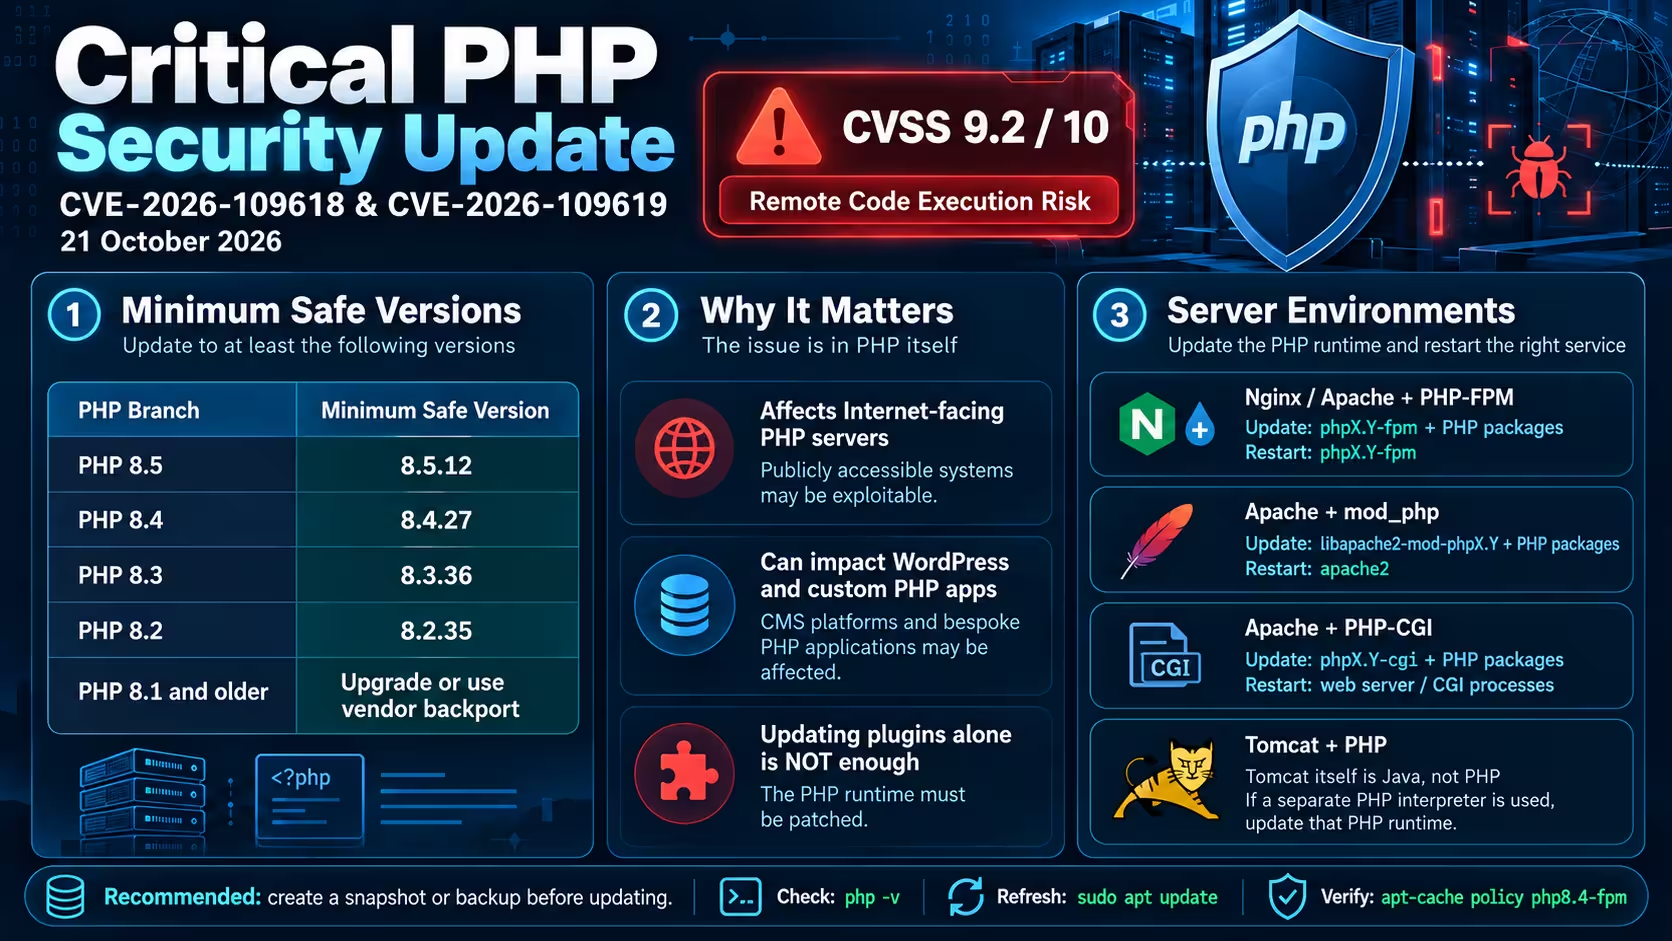
Critical PHP Security Update: Fix CVE-2026-109618 and CVE-2026-109619
Published: October 22, 2026 | Severity: Critical — CVSS 9.2/10 [...]